Key Notes
- Binance targets a withdrawal restart within 40 hours of Friday’s address, subject to rigorous testing of its rebuilt infrastructure.
- More than $6.34 billion in company funds is reserved for losses, including $5 billion already held in affected tokens, Teng says.
- A full Proof of Reserves report is planned for Monday, November 2, as the investigation expands beyond an initially suspected laptop breach.
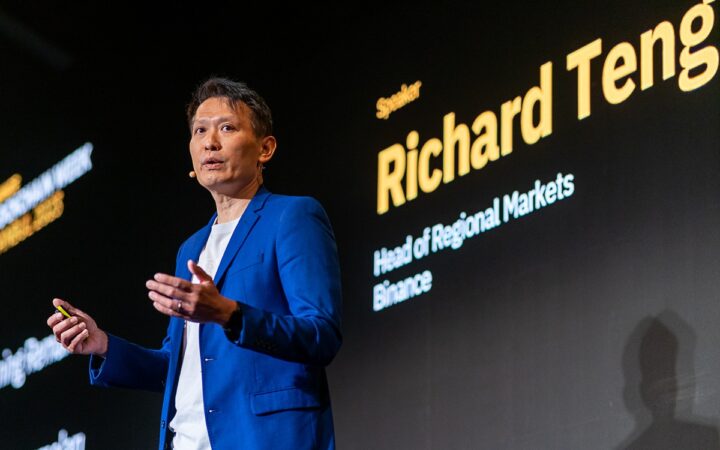
Binance aims to restore withdrawals within 40 hours of co-CEO Richard Teng’s Friday video update, as the exchange rebuilds its infrastructure following a multibillion-dollar hack. The target points to Sunday, November 1, but Teng said services would remain suspended until the system passes rigorous testing.
In the October 30 address, Teng said Binance had reserved more than $6.34 billion of company funds to cover stolen assets, with $5 billion already held in the affected cryptocurrencies. He also promised a full Proof of Reserves report by Monday, November 2, and said investigators had discovered additional breach points beyond an initially suspected compromised laptop.
A message from Binance’s Co-CEO, @_RichardTeng.
— Binance (@binance) October 30, 2026
Withdrawal Restart Depends on Security Testing
Teng described the restart as a recovery target rather than a completed restoration. Binance is rebuilding and retesting its withdrawal infrastructure after the attackers obtained execution authority over a hot wallet without passing through the company’s normal approval controls.
The 40-hour estimate runs from Friday’s address, which Binance shared shortly after 14:30 UTC. It is not a new countdown beginning when this article is published. CoinScreamer’s withdrawal update also details the Sunday target and the separate timetable for public reserve verification.
For customers, restoring the ability to move assets is the immediate operational milestone. Reopening withdrawals, completing replacement-token purchases and recovering stolen funds are separate tasks, however, and Teng did not say that all three had been completed.
Binance Reserves $6.34 Billion in Company Funds
Teng reiterated that Binance would cover hacked losses using its own resources. He said the exchange retained much of its operating earnings in crypto assets, allowing it to absorb the loss from company holdings while acquiring the remaining affected tokens through market and over-the-counter transactions.
The distinction between a dollar allocation and the underlying token inventory matters. Binance says $5 billion is already held in the exact assets affected; that does not mean the entire amount was newly purchased following the breach. The outstanding purchases are intended to address the remaining token shortfalls.
As CoinScreamer reported, Binance’s earlier funding announcement excluded roughly $3 billion in frozen or protected assets from the company-fund allocation. Those restricted assets belong to the separate recovery effort and should not be counted as another theft on top of the reported loss.
Teng said the attack affected Binance’s own hot wallet and that customer funds were not used or affected. He described the vast majority of customer assets as held in cold wallets. Those assurances remain the exchange’s account, with the promised public reserve report still ahead.
Investigation Finds Additional Breach Points
The investigation has moved beyond the initial theory involving a compromised employee laptop. Teng said additional points of breach had been identified and described a coordinated attack involving more than one person.
He also said the attackers used self-destruct mechanisms that removed tools and traces, complicating the investigation. That claim concerns evidence available to investigators; it does not mean public blockchain transaction records have disappeared.
According to Teng, the attackers used EIP-7702 to obtain on-chain execution approval over the hot wallet outside Binance’s normal controls. The Ethereum specification allows an account to delegate execution to contract code through signed authorization. It is a code-delegation mechanism, rather than a conventional multisignature wallet protocol.
CoinScreamer’s technical brief examines 50 authorization entries preceding the Ethereum wallet drain. That sequence provides evidence about the Ethereum transactions, while leaving unanswered how the signatures were obtained and how other affected networks were compromised.
Full Reserve Report Is Promised for Monday
Binance plans to complete the remaining asset purchases and verify holdings through Proof of Reserves. Teng said a full report would be shared by Monday, November 2, with an initial view potentially available earlier.
The report is a future disclosure, not proof already delivered in the video. Its scope and supporting information will determine what users can check about their balances and the assets backing them. Teng did not publish a wallet-by-wallet reconciliation in the address.
The company is also reviewing security across endpoints, cloud infrastructure, key management and transaction signing. That broader review reflects the additional breach points identified during the investigation.
Frozen Assets Remain Part of the Recovery Effort
Teng said Binance was working with law enforcement, blockchain intelligence firms, token issuers and other exchanges to trace and recover funds. CoinScreamer’s Tether brief documents the issuer’s earlier confirmation that more than $1.567 billion in USDT had been frozen in connection with the incident.
A freeze restricts an asset’s movement; it does not by itself establish that the money has been returned. As we previously reported, the scale of the theft makes both replacement funding and recovery central to Binance’s response.
The next checkpoints are therefore concrete: whether withdrawals reopen after testing, whether the remaining token purchases are completed, and what the promised reserve report shows. Friday’s video sets those targets without establishing that the recovery is finished.